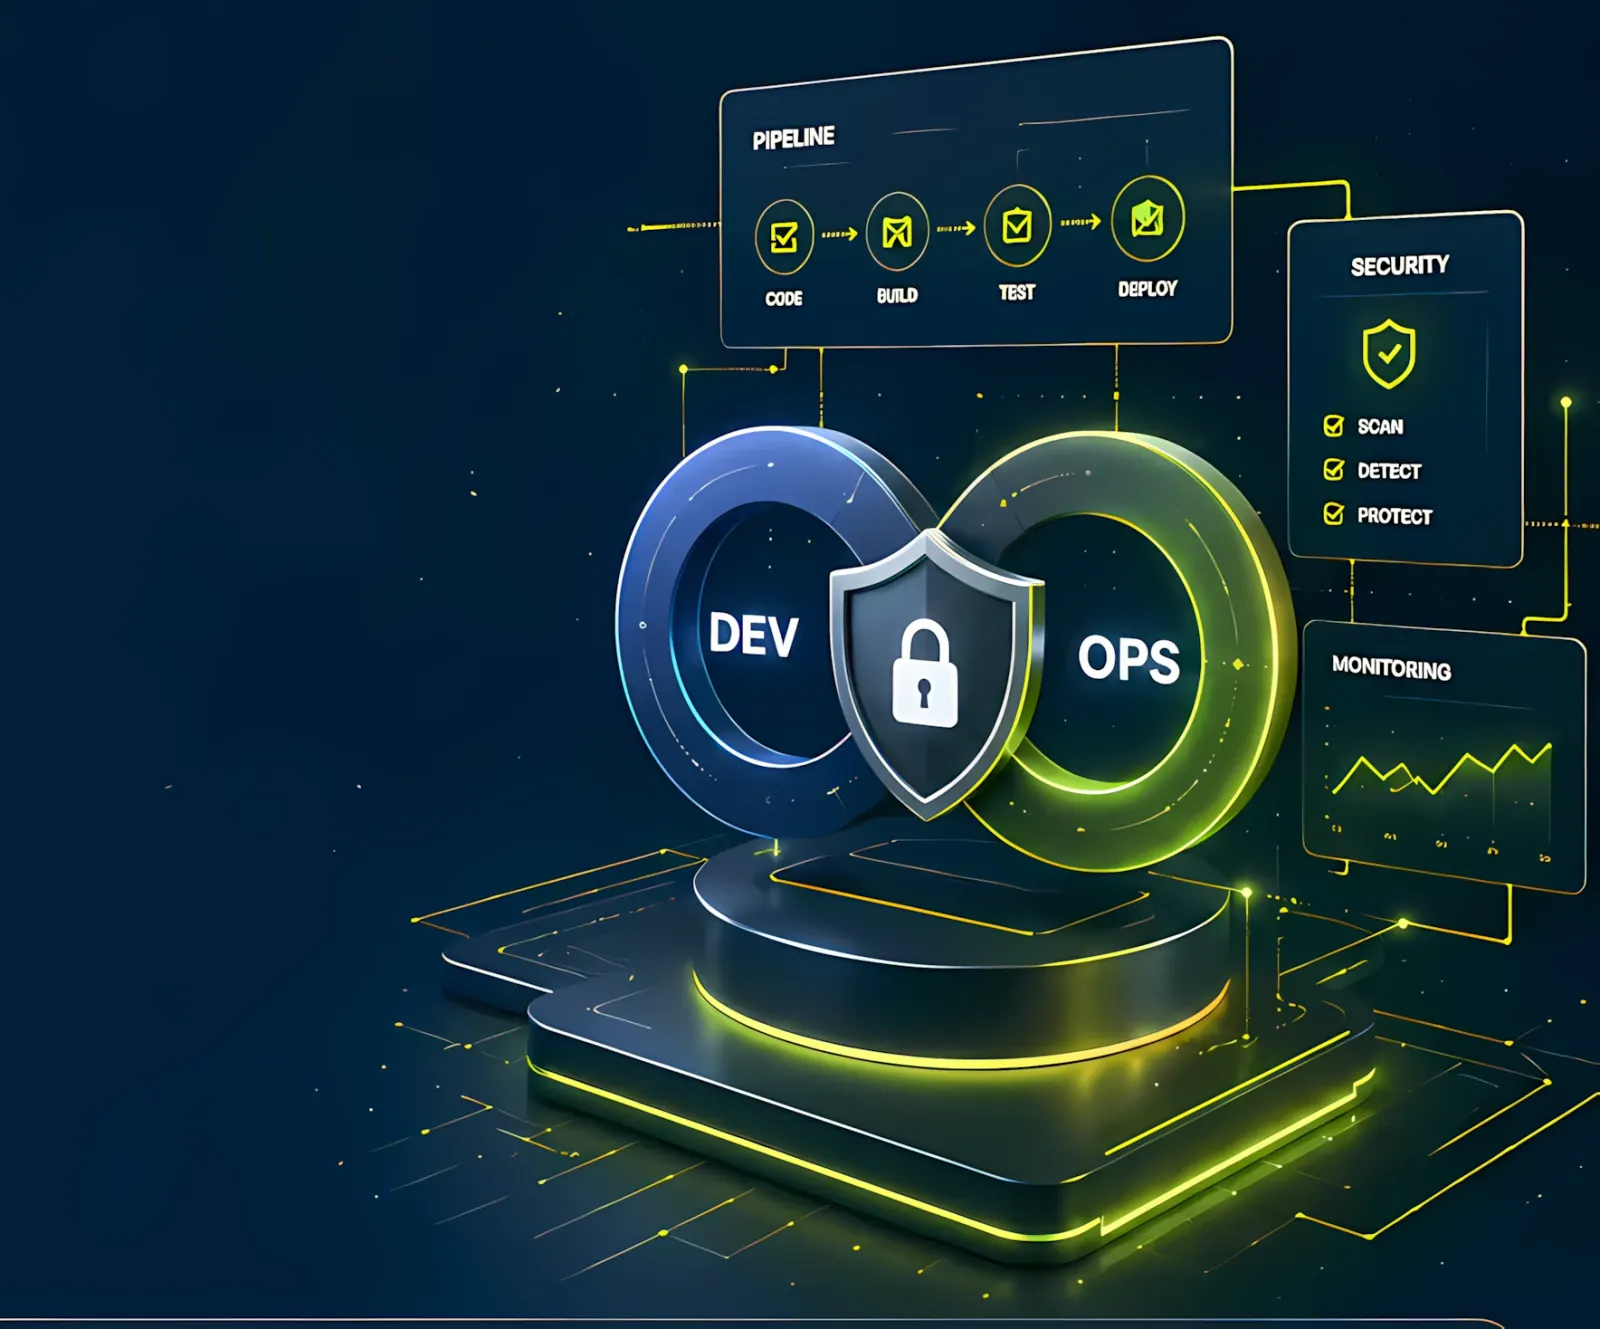
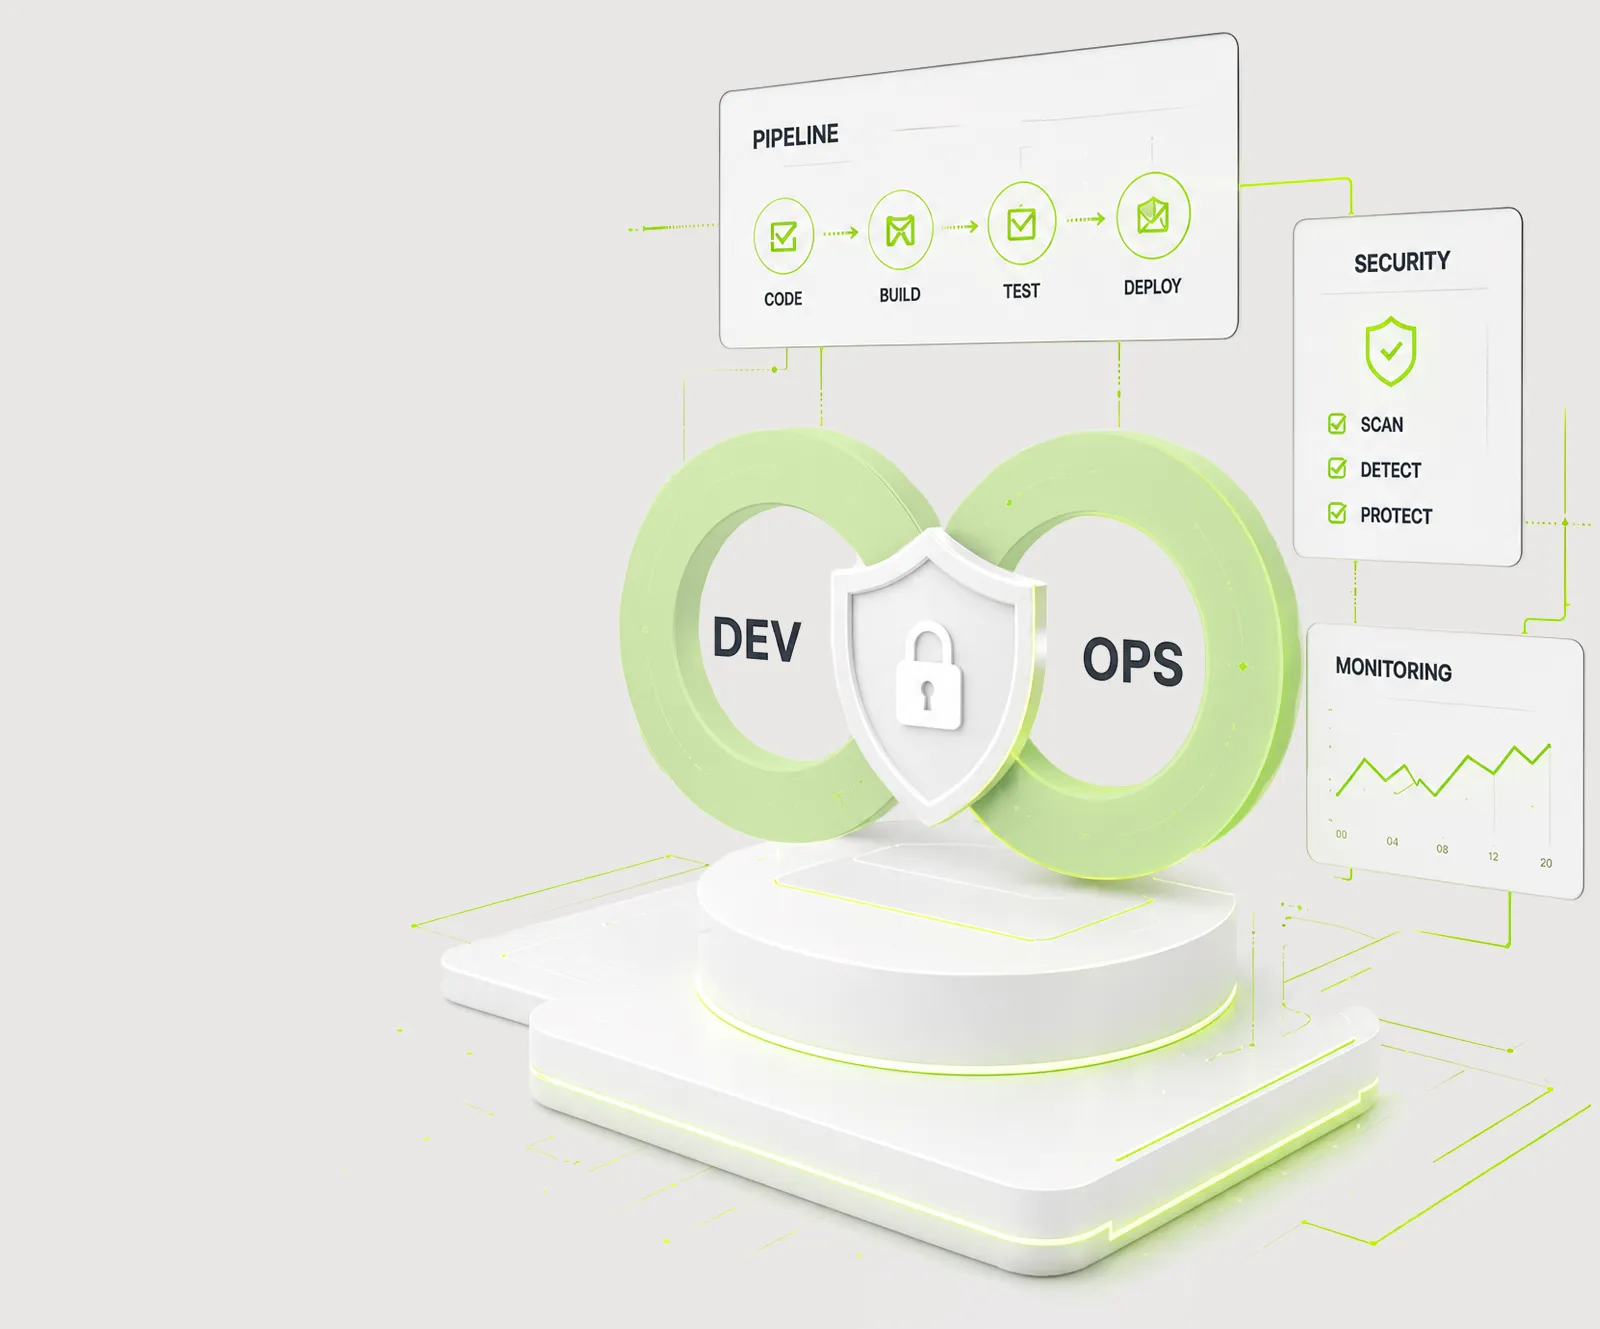
Modern enterprises in Dubai are racing to ship software faster without compromising on security or compliance. Our DevSecOps services in Dubai are built to close that gap — embedding security directly into every stage of your software delivery pipeline, from the first commit to production deployment, rather than treating it as an after thought.
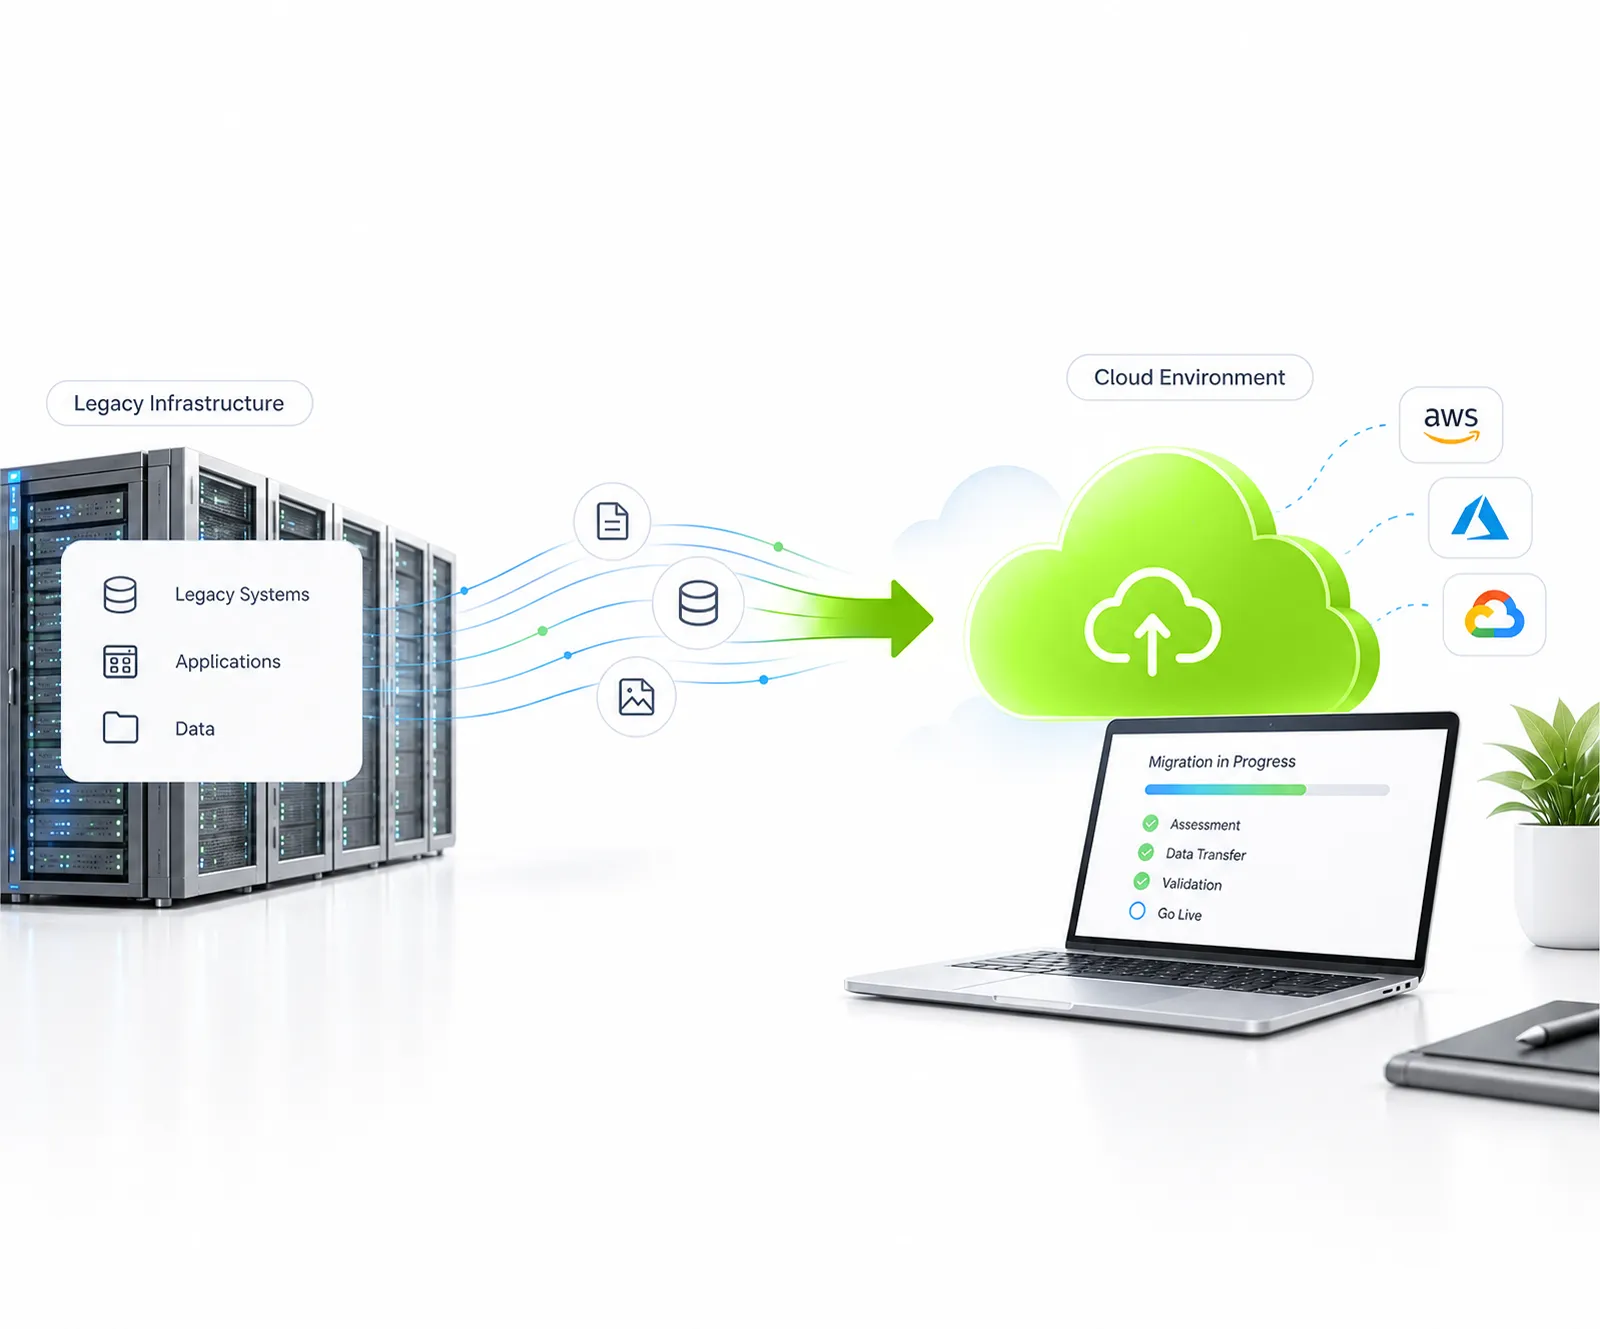
This is the one place we'll say it in full, so the rest of our cloud pages don't have to repeat it our engineers hold certifications and designations across every leading public cloud vendor, and our DevOps practice adapts to which ever platform your workloads already live on rather than forcing a migration to get support.
industry-proven solutions across the cloud computing and application lifecycle, from first adoption through 24×7 operational management, leveraging automation and analytics for business value.
end-to-end services for teams building critical business solutions on Azure's cloud-native capabilities, with 24×7 operational management of your Azure environments.
deep expertise and automated blueprints that pinpoint where to start based on your business needs, legacy systems, in-house expertise, and cloud objectives, backed by 24×7 GCP operational management.
full-range cloud products for databases, networking, security, analytics, and big data, including Elastic Compute Service (ECS) for elastic, secure virtual cloud servers.
Dubai's digital economy — spanning fintech, government services, logistics, and e-commerce — operates under strict regulatory scrutiny, including UAE data protection laws and sector-specific compliance mandates. A single security gap in a fast-moving release cycle can expose sensitive data, disrupt operations, or trigger regulatory penalties. Our DevSecOps approach ensures security controls, automated vulnerability scanning, and compliance checks run continuously and automatically, so speed and safety are never a trade-off.
We deliver end-to-end DevSecOps enablement tailored to your existing technology stack:
Integrating static and dynamic application security testing (SAST/DAST) directly into your build and release pipelines.
Scanning Terraform, CloudFormation, and Kubernetes manifests for misconfigurations before deployment.
Image scanning, runtime protection, and policy enforcement across containerized workloads.
Centralized secrets vaulting and least-privilege access controls across your cloud and on-prem environments.
Automating audit trails and policy enforcement aligned with regional and industry compliance frameworks.
Real-time detection and automated remediation workflows across your DevOps toolchain.
Our engineers assess your current SDLC, identify security gaps in your pipeline, and design a phased rollout — starting with quick wins like automated dependency scanning, then progressing to full policy-as-code enforcement. We work with teams using GitLab, GitHub Actions, Jenkins, Azure DevOps, AWS, and Kubernetes-native environments, adapting our tool chain to fit yours rather than forcing a rebuild.
Beyond the security layer, we implement the practices that make continuous delivery actually continuous:
automating your build, test, and deployment cycles for faster, more reliable releases.
managing and provisioning infrastructure through machine-readable definition files, not manual console clicks.
real-time visibility into application performance and infrastructure health.
standardizing environments with Docker and orchestrating at scale with Kubernetes.
Every engagement follows a consistent, six-step process from first assessment through steady-state operations:
building an assessment roadmap that visualizes your desired end state against traceable metrics.
an experienced team builds against continuous, recorded git practice from day one.
new functionality is integrated into your existing infrastructure using tools like Jenkins.
continuous automated testing, including container-based simulation, with feedback analyzed and acted on before release.
finalized code ships to production through robust CI/CD tooling built for consistent, repeatable performance.
24/7 monitoring with a dedicated team for early error detection and prompt remediation.
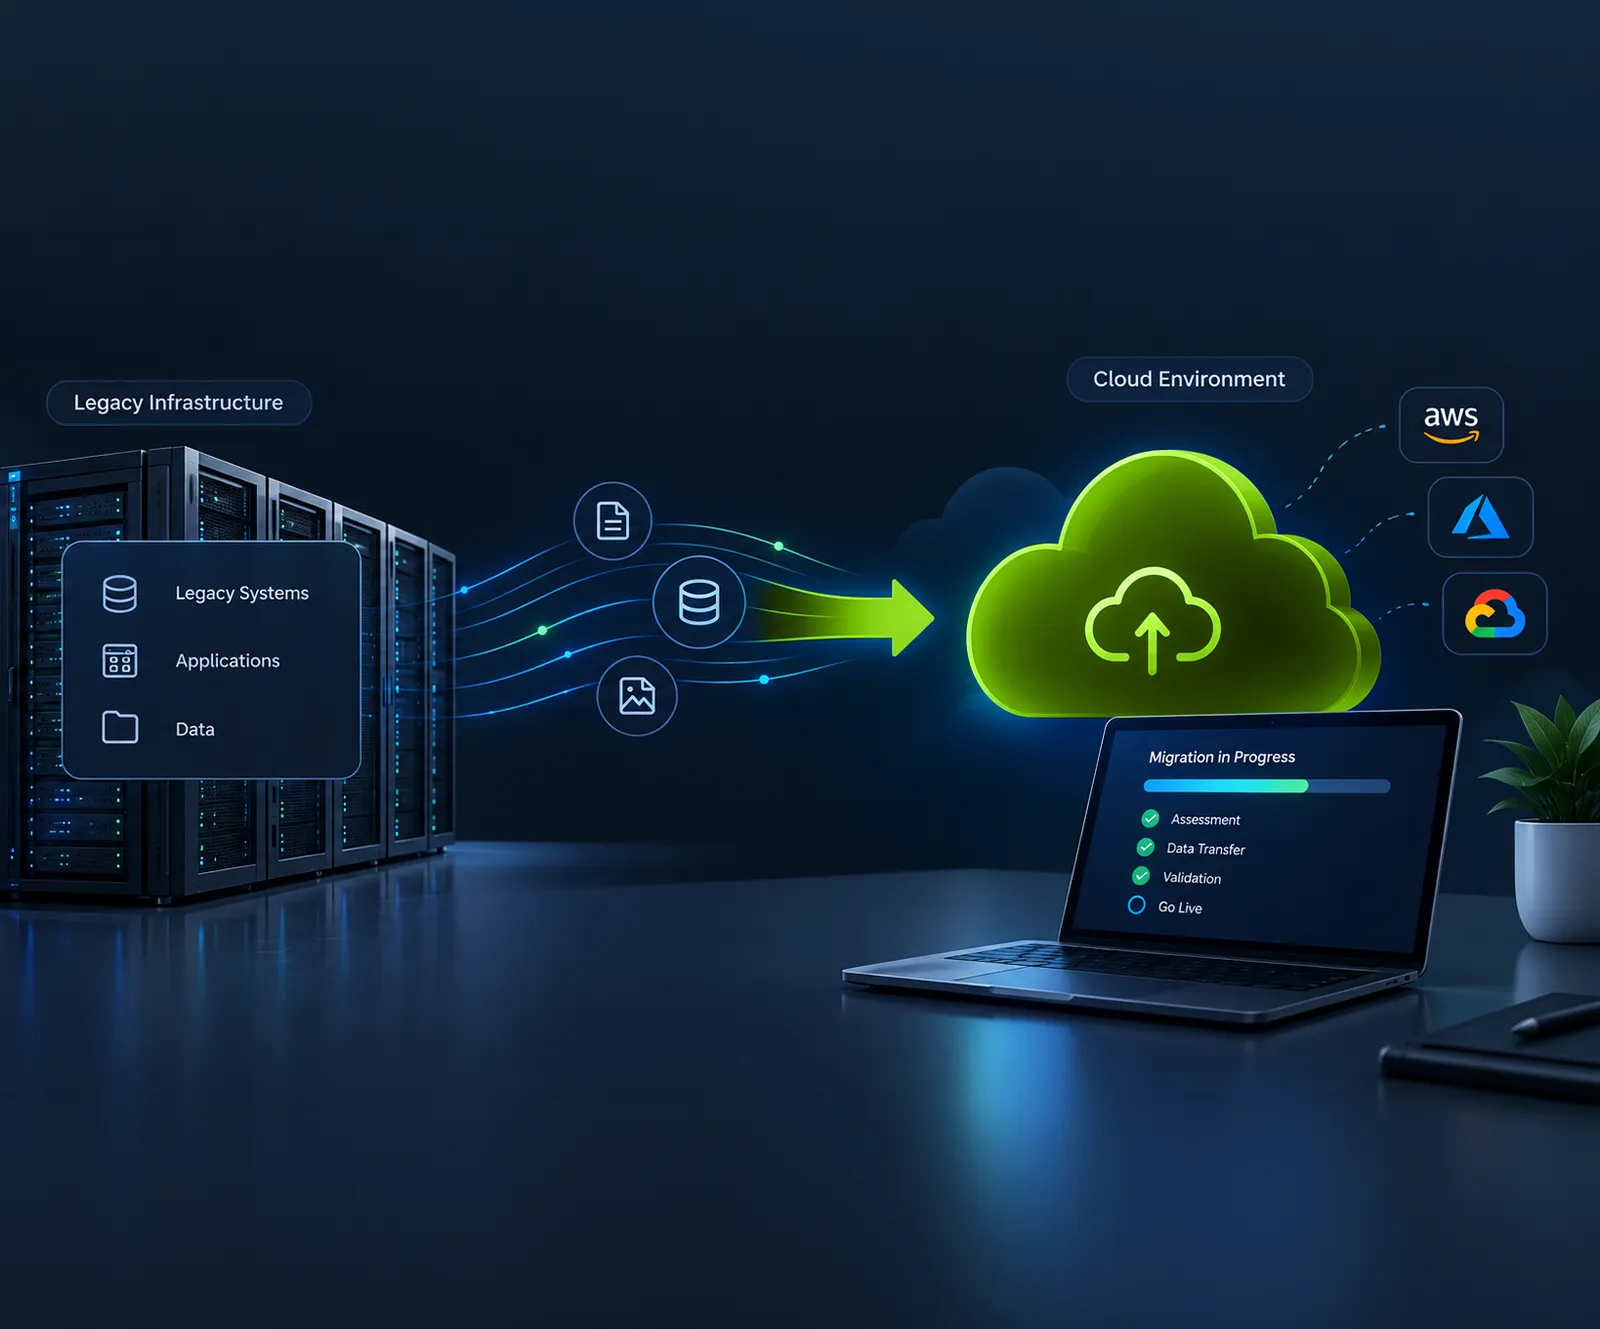
From government-linked entities to fast-scaling fintechs and enterprises modernizing legacy infrastructure, we tailor DevSecOps delivery to the realities of operating in Dubai — where regulatory scrutiny is high and market speed is non-negotiable. Our team pairs deep technical DevSecOps expertise with regional compliance fluency, so every pipeline we build is audit-ready by design, not by retrofit. The outcome is measurable shorter release cycles, fewer exploitable vulnerabilities reaching production, and infrastructure your compliance team can stand behind — all without adding friction to how your developers ship code. Choose a DevSecOps partner that treats Dubai's regulatory demands and business velocity as equally non-negotiable, and turn security into a growth enabler rather than a gate.
AI-Driven DevSecOps in Depth
Common questions about DevSecOps Services in Dubai.
A.Yes — our teams hold certifications across AWS, Microsoft Azure, Google Cloud Platform, and Alibaba Cloud, and we regularly support businesses running genuinely multi-cloud or hybrid environments rather than a single vendor.
A.We adapt to your existing toolchain rather than forcing a rebuild — commonly GitLab, GitHub Actions, Jenkins, Azure DevOps, Docker, and Kubernetes, integrated with the cloud platform(s) you already run on.
Explore More
Tell us about your project and our team will get back to you to map out the fastest path to a secure, scalable solution.